Audit software for IT auditors and certification bodies
The Secure Audit Platform supports the execution of the audit: audit programme, information requests, evidence, sampling, findings, review and report in one place. Built by IT auditors and used in our own audits.
The file is built during the audit, not afterwards
Most audit software is made for the organisation being audited. This platform is made for the auditor. The audit programme is the backbone: every information request, every piece of evidence, every sample and every finding is attached to a line in it. At the end of the audit the file is complete without you having to assemble it, and the reviewer can see per line what the conclusion rests on.
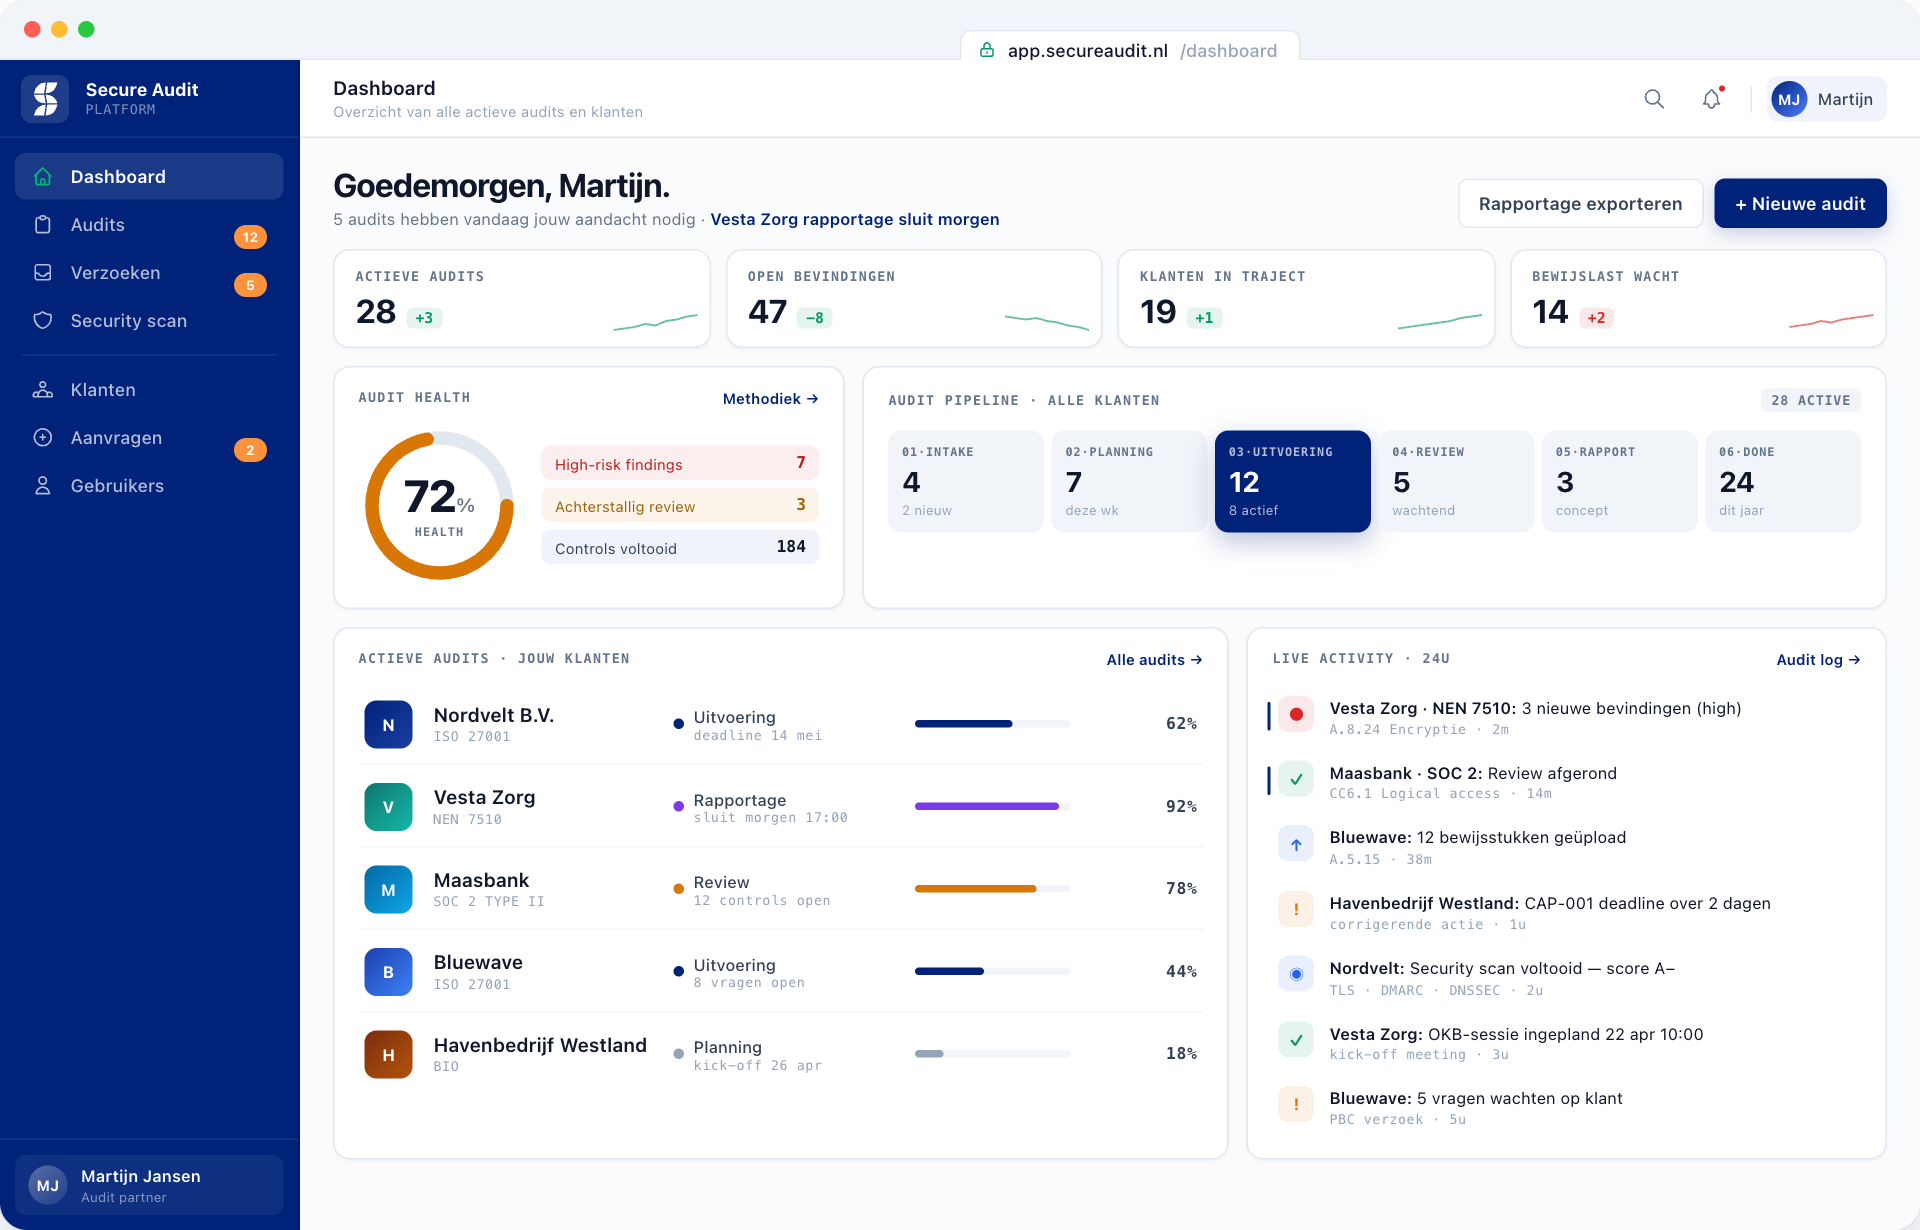
The auditor dashboard: active audits per phase, open findings, evidence awaiting review and the activity of the last 24 hours.
Who is the platform for?
For anyone who performs audits and has to account for the file afterwards: to a reviewer, to an accreditation body or to a client's external auditor. The organisation being audited takes part through the client portal and needs no licence of its own.
Looking for support with your own certification or assurance report instead? See our IT audit services; you work in the same platform, with us as the auditor.
Eight components, one audit programme as the backbone
Every component hangs off the lines in the audit programme. That is why a reviewer can see per line, at the end, which request was made, which evidence was received, which sample was drawn and which conclusion followed.
Audit programme and standards library
Start from a predefined audit programme or import your own lines. For each line you record design, implementation and operating effectiveness separately, with the test procedures alongside. Framework mapping links lines from different standards for an integrated audit.
Information requests
Generate the request list from the audit programme, set deadlines, send reminders and see per request what is open, what has been answered and what is waiting for your review. The client sees the same list in their portal.
Evidence per line
Evidence arrives against the request and is thereby attached to the line in the audit programme. You approve it, reject it with a comment or mark it as expired. Files are validated on type at upload.
Sampling
Import the population, have the sample size calculated and draw the sample at random inside the platform. Test results per item are recorded directly against the line, so the basis for your conclusion is in the file.
Findings and corrective actions
Findings get a type, a status and an owner. For each finding the client can complete a corrective action plan, also through a secure share link for someone without an account. You assess the action and its execution.
Review and certification decision
A reviewer with a dedicated role assesses the file, signs off review work and takes the certification decision. The checklist for that decision follows the requirements per audit type, and memos such as the independence declaration have their own sign-off step.
Scheduling and audit duration
Audit scheduling with a day plan per auditor, exportable to your calendar and to Excel. For certification audits the platform calculates audit duration on the basis of ISO/IEC 27006, including sites and site visits.
Reporting and file
Internal report and client report as Word or PDF, the status of information requests as an overview, and the complete file as a ZIP. Certificates are generated as PDF from the certification cycle.
How an audit moves through the platform
The platform follows the phases of a certification audit under ISO/IEC 17021-1 and of an assurance engagement under ISAE 3402 or ISAE 3000. For an internal audit you skip the steps you do not need.
The client sees only what is meant for them: open requests, the schedule, their corrective actions and their certificates. Evidence is uploaded against the request, after which it is queued for your review. Email notifications keep both sides informed of deadlines and responses.
For controls that produce evidence monthly, quarterly, half-yearly or annually, you set up a monitoring period. The client submits per period, you approve, and at the next audit or surveillance the evidence for the whole period is already there.
Independence declaration, planning memo, closing memo and other standard file documents are available as templates and move through draft, completed, review and signed off. At an accreditation assessment it is visible who established what and when.
Predefined audit programmes per standard
Each standard is available as an audit programme with the requirements from the main text and, where applicable, the controls from the annex. You tailor it to the scope and add your own lines. For ISAE 3402 and ISAE 3000 you build the audit programme from the client's control objectives.
Integrated audits
With framework mapping you link lines from different standards to each other, for example an ISO 27001 Annex A control to the corresponding criterion in SOC 2 or NEN 7510. A piece of evidence is then requested once and counts for both. How to set up such an audit is covered in integrated audits across multiple standards.
Built the way we would test it ourselves
An audit platform holds your clients' evidence. The measures below are the measures we would expect to find at a client, and they are in the code, not only in a policy document.
Roles and tenant separation
Auditor, reviewer, administrator and client users each have their own permissions. A client sees only its own audits; a reviewer can assess but not execute.
Two-factor authentication and SSO
Sign in with password plus authenticator app, or through Microsoft Entra ID or Google for existing accounts. Repeated failed attempts are blocked.
Audit trail
Every change is recorded with user, timestamp, entity and the old and new value. That log cannot be edited or deleted from within the application.
Look along without touching
An administrator at the audit firm can temporarily view the environment of a client user in strict read-only mode, to answer a question without changing anything.
Integrations if you want them
SharePoint and OneDrive can be enabled per organisation to link files. Tokens are stored encrypted. The module is off by default.
Security in the delivery pipeline
Static analysis, an OWASP Top 10 scan, secret scanning and a dependency check run on every code change before it can reach production.
Want to assess the technical set-up in detail before putting client data in the platform? That is a normal question from an audit firm. Request the security documentation.
Made by auditors who work in it themselves
Our own audits as the test environment
Secure Audit runs its own audit engagements in this platform. Whatever does not work in practice, we notice first and change.
Designed around the requirements on the file
Reviewer role, sign-off, a certification decision with a checklist per audit type and an audit trail that cannot be altered: the requirements an accreditation body or a quality review places on a file are built into the workflow.
Dutch and English
The interface is available in Dutch and English, so an international client can take part in its own language. The texts of Dutch frameworks (NEN 7510, BIO, DigiD) are in Dutch. Support comes from the auditors who build the platform.
Your own branding
Your firm's name, logo and colours in the platform and in the generated reports, so the client experiences it as your environment.
Frequently asked questions about the platform
How we audit, in the knowledge base
The platform follows the way of working described in these articles. Read them to see whether it matches how your firm works.
Evidence in an IT audit
→What an auditor accepts as evidence, and why the population matters more than the sample.
Audit readiness assessment
→The dress rehearsal for the audit, and how it differs from a gap analysis.
The Type II observation period
→Why you build the evidence during the period rather than afterwards.
ISO 27001 certification step by step
→From scope to stage 2 and the three-year cycle, seen through the auditor's eyes.
Internal audit: annual plan and programme
→How to set up an audit programme that a certification auditor accepts.
Continuous auditing
→What continuous testing is and is not, and when it makes sense.
See the platform on a real audit
In half an hour we walk through an example audit, from audit programme to certification decision. Bring your own standard or audit programme if you want to see how it fits.